Team & expertise

A proof is only as good as the people who sign it.

S.AI.F is staffed by evaluators, cryptographers, offensive-security engineers and regulators who have done this work inside national institutions, frontier labs and audit firms — not by generalists reading a checklist.

ILLUSTRATIVE PROFILE DATA · REPLACE BEFORE PUBLICATION
27
Core specialists, employed — plus 60+ accredited associates on call
180yrs
Combined practice in evaluation, security and regulation
4
Standards bodies where our people hold seats or contribute text
11
Jurisdictions engaged across EU, GCC, UK and APAC

Practice leadership

Six practice leads. Each owns a discipline end to end and personally signs the findings that leave under their name — the signer is never the person who built the thing.
Dr. Amina R., Chief Validation Officer

Dr. Amina R.

Chief Validation Officer

Twelve years designing measurement regimes at a national metrology institute, then model evaluation for a frontier lab. Built the sealed-evaluation methodology S.AI.F runs today.
PhD StatisticsISO/IEC SC 4214 papers
Marc D., Head of AI Security

Marc D.

Head of AI Security

Eighteen years in offensive security, latterly running red team operations for a tier-one cloud provider. Leads our GPU-estate assessments and the AI Factory SOC build-out.
OSCPCISSPOWASP LLM contributor
Dr. Hélène V., Director of AI Policy

Dr. Hélène V.

Director of AI Policy

Former supervisor at a European financial regulator; drafted sectoral guidance now cited by two national authorities. Translates regulation into control sets engineers can implement.
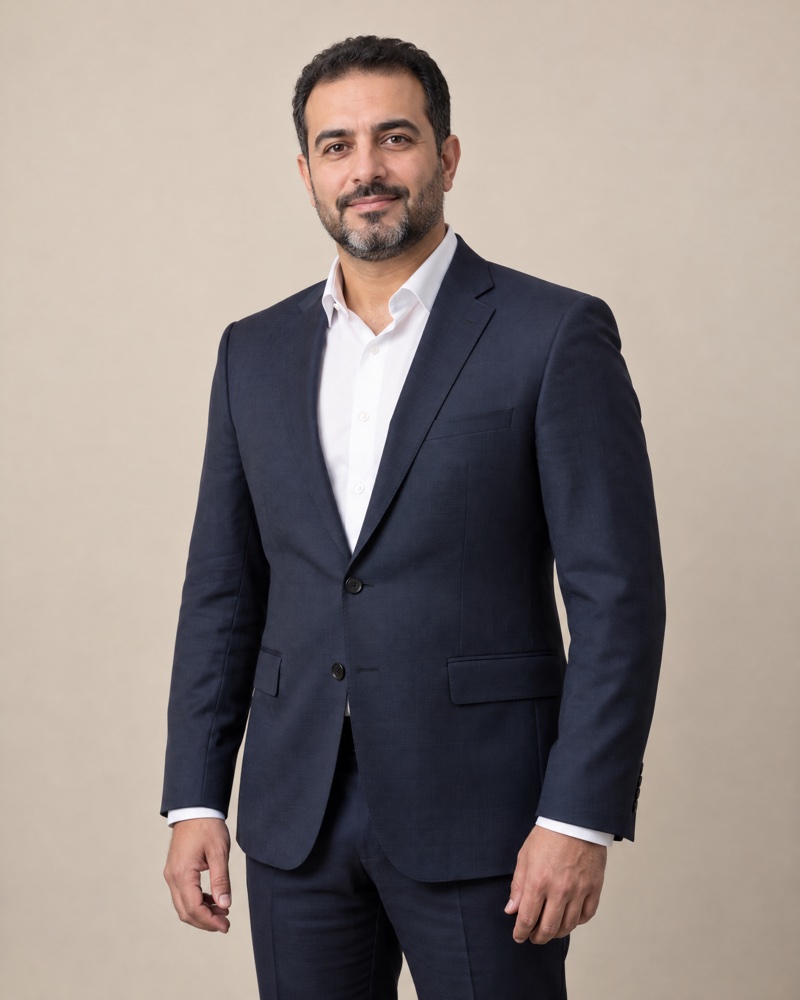
PhD LawCEN-CENELEC JTC 21CIPP/E
Omar K., Principal Cryptographer

Omar K.

Principal Cryptographer

Post-quantum migration lead for a national payments network. Owns the certificate format, the HSM-backed signing chain and our harvest-now-decrypt-later threat modelling.
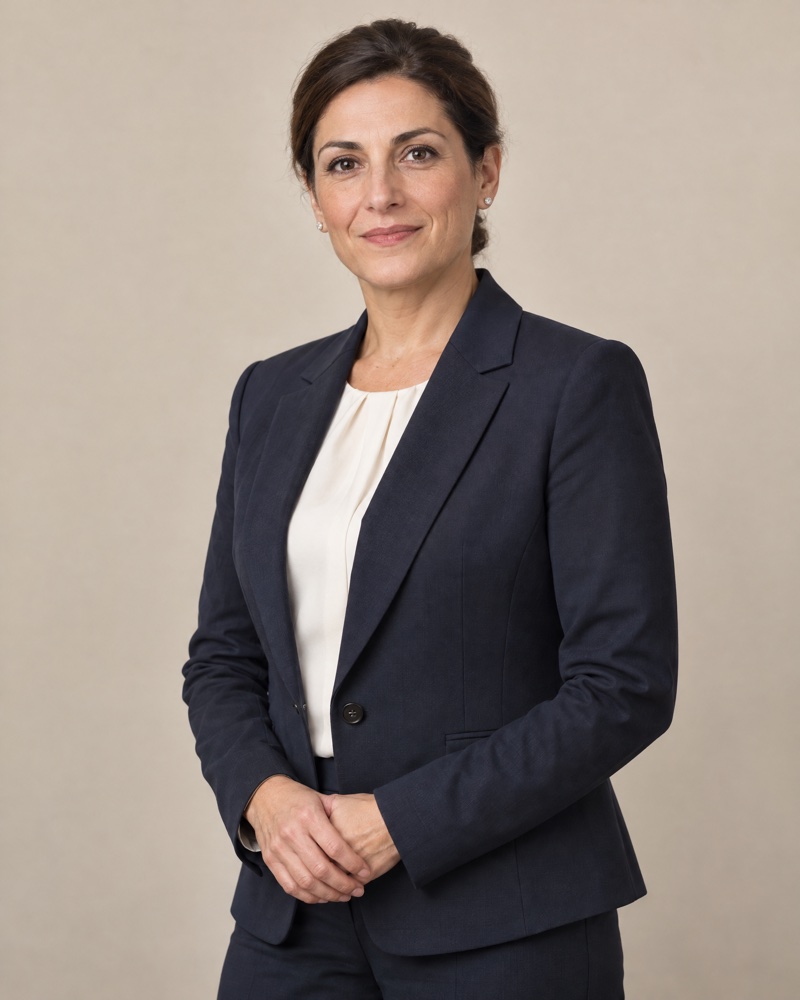
IETF contributorML-KEM / ML-DSAHSM / FIPS 140-3
Sofia L., Head of Assurance & Audit

Sofia L.

Head of Assurance & Audit

Fifteen years of regulated-industry audit at a Big Four firm. Runs independence, evidence standards and the sign-off gate — nothing is certified without her opinion on file.
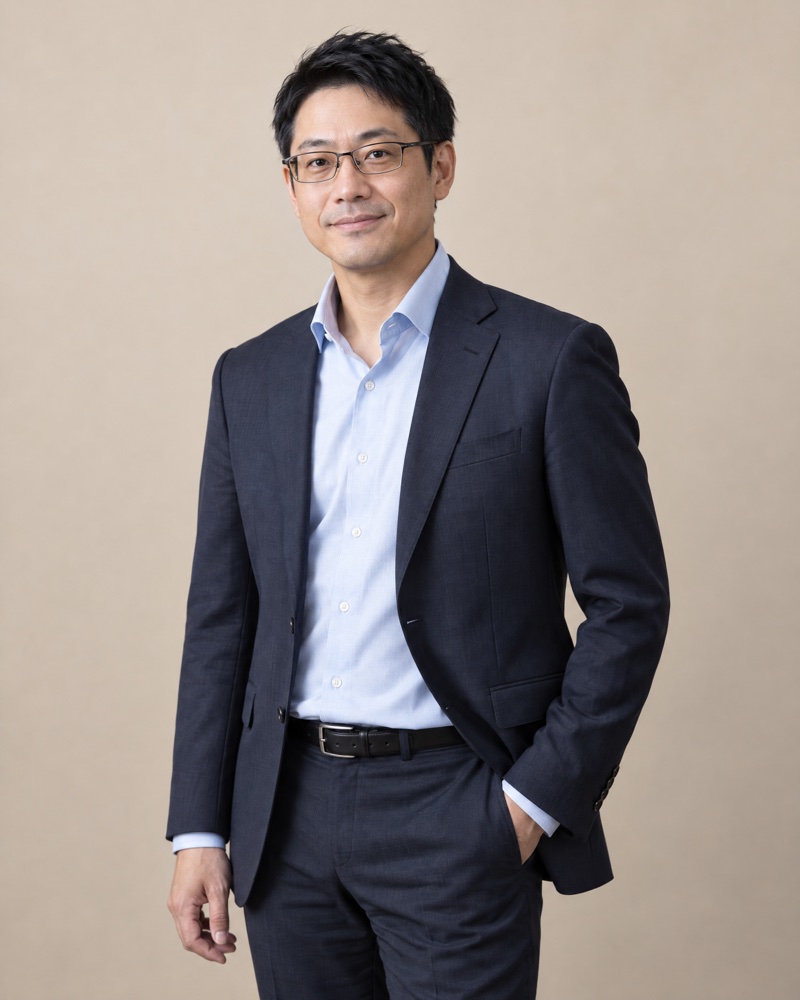
ISO/IEC 42001 LACISAChartered accountant
Dr. Kenji T., Principal ML Engineer

Dr. Kenji T.

Principal ML Engineer

Built evaluation infrastructure for models at the hundred-billion-parameter scale. Runs our confidential-compute harness so tests execute without anyone seeing plaintext weights.

PhD Computer ScienceTDX / SEV-SNPZKML
Depth of bench

Every discipline covered in-house, not subcontracted.

The bar shows how much of each discipline we deliver with employed staff. Where coverage is deliberately partial — sector-specific clinical or legal judgement — we bring named associates under the same independence rules and disclose them in the engagement letter.

In-house coverageAccredited associates
AI validation & evaluation6 · 2 principal
AI security & confidential compute5 · 2 principal
Policy, audit & assurance5 · 2 principal
ML engineering & platform5 · 1 principal
Cryptography & post-quantum3 · 1 principal
Sector specialists · finance, health, public3 · 1 principal
Where our people sit

We help write the rules we audit against.

ISO/IEC JTC 1/SC 42 — national-body experts on AI management and impact assessment.
CEN-CENELEC JTC 21 — contributors to harmonised standards under the EU AI Act.
IETF — draft contributions on supply-chain transparency and signed attestations.
NIST AI RMF & PQC community — profile feedback and migration practice.

Credentials held across the team

6 × PhD5 × ISO/IEC 42001 Lead Auditor6 × ISO/IEC 27001 Lead Auditor4 × CISSP3 × OSCP3 × CIPP/E2 × CISA2 × CCSP31 certifications in total
Every engagement member is security-cleared and conflict-screened before scoping.
Signers rotate off a client after two consecutive certification cycles.
Continuing education: 40 hours per person per year, audited internally.

How we staff an engagement

You get a named pod, not a rotating bench. Composition is fixed at kick-off and published in the engagement letter — including who signs and who is independent of the build.

Validation sprint

One model, one intended purpose, one signed result. The pod runs the sealed evaluation set, opens findings against declared thresholds, and hands the certificate to an independent signer who took no part in the testing.

Duration
6 weeks
Pod size
4.4 FTE
Cadence
Weekly gate
Leaves behind: Signed Trust Proof, findings register with owners and SLAs, re-runnable evaluation package.
EL
Engagement lead
Scope, thresholds, client governance
0.3
VA
Validation architect
Methodology and evaluation design
1.0
EE
ML evaluation engineers ×2
Harness, runs, confidential compute
2.0
FS
Fairness & statistics lead
Group metrics, calibration, power
0.5
AR
Assurance reviewer
Evidence standard and working papers
0.4
IS
Independent signer
Certifies; independent of the build
0.2

Meet the people who would sign your proof.

A 45-minute session with the practice lead for your domain — no sales engineer in the room. Full CVs and independence declarations are shared under NDA before scoping.

Book a demoSee the work →